Institutional-Grade Security for High-Stakes Legal Data
Prove to your corporate clients and class members that their most sensitive information is impenetrable.
Corporate Clients Demand Proof of Cybersecurity Maturity
Corporate clients now demand rigorous proof of cybersecurity maturity before awarding business. In an era where a single breach can expose trade secrets, M&A strategies, and the personal information of thousands, law firms can no longer treat security as an IT afterthought.
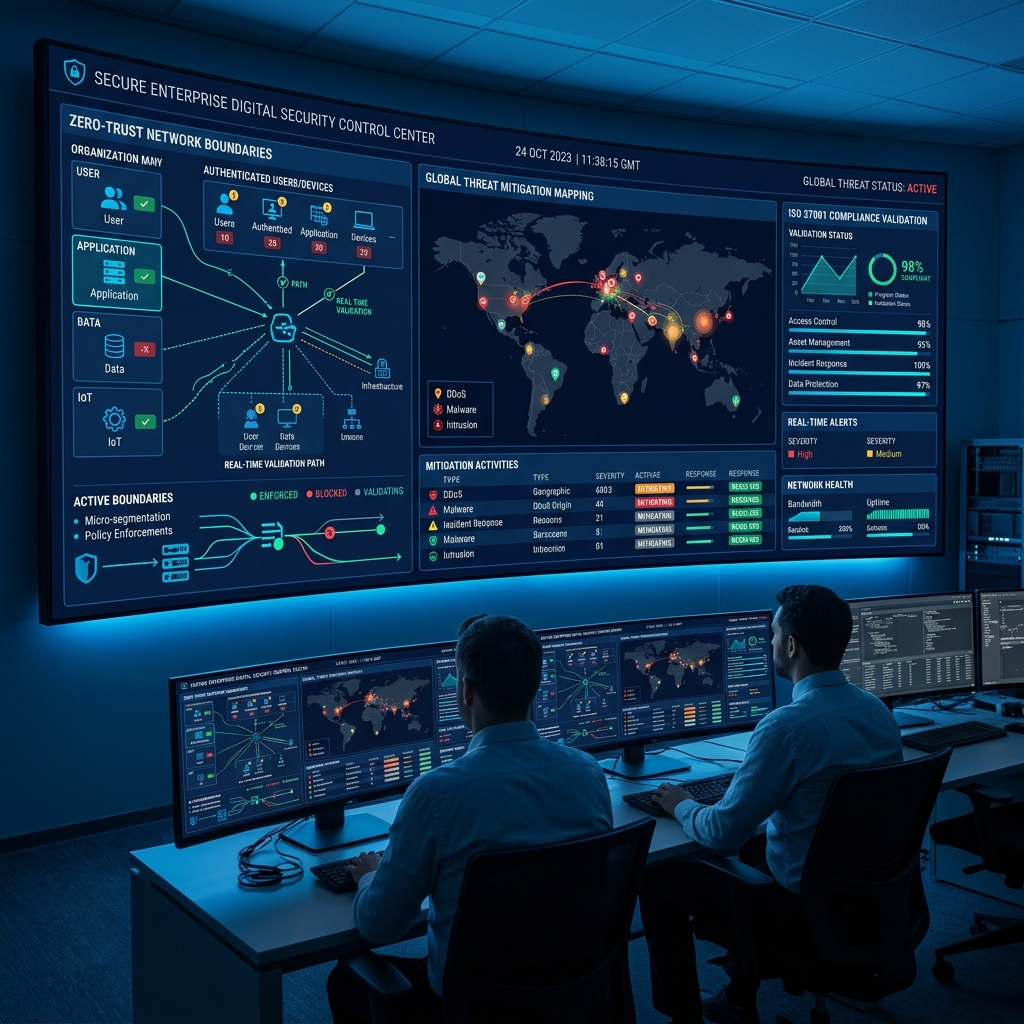
We establish robust governance frameworks tailored to protect high-stakes legal and financial data. By aligning enterprise cybersecurity strategies with your firm's profitability goals, we ensure continuous, rigorous compliance with ISO 27001 and NIST standards. Our approach transforms cybersecurity from a cost center into a competitive advantage that wins and retains premium client relationships.
From cross-functional incident response planning to zero-trust architecture design, we deliver the institutional-grade security posture that today's most demanding corporate clients require.
ISO 27001 & NIST Alignment
End-to-end compliance lifecycle management—from gap analysis through certification and continuous monitoring.
Cross-Functional Incident Response
Unified response framework integrating IT, legal, compliance, and executive leadership for rapid threat neutralization.
99.999% Availability
Highly available infrastructure with redundant systems, automated failover, and continuous monitoring.
Successfully neutralized potential threats by 50% while protecting highly sensitive client data and maintaining 99.999% virtual infrastructure availability across all critical systems.
Request a Security Architecture Audit
Our senior security team will evaluate your firm's cybersecurity posture against ISO 27001 and NIST frameworks—identifying gaps, quantifying risk, and delivering a prioritized remediation roadmap.